Firebase API Key Exposed on GitHub: Is It Actually a Problem?
Your Firebase API key is on GitHub, and GitHub — or a scanner, or a worried teammate — has flagged it. The short answer is: usually not a problem by itself, but it is a problem if the things behind the key are not locked down. The key is not a password. It is a […]
How to Hide an API Key From the Browser Network Tab (and Why You Can’t)
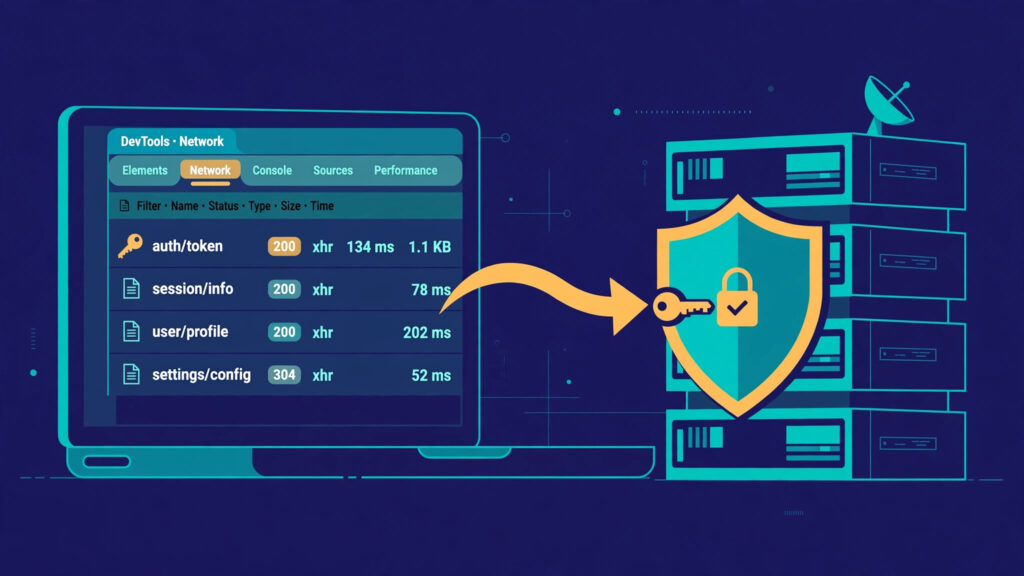
How to Hide an API Key From the Browser Network Tab (and Why You Can’t) You cannot hide an API key from the browser’s Network tab if the browser itself sends that key. The Network tab is not a leak in the browser. It is the browser showing its owner exactly what it sent and […]
Free Security Scanner for Vibe-Coded Apps: Check Yours in 60 Seconds
A vibe-coded app can work perfectly and still be open. That is the whole problem: an AI builder will happily ship a working sign-in page, a working dashboard, and a database that answers anyone who asks. Nothing breaks, so nothing warns you. A free security scanner is the fastest way to find out whether that […]
Supabase Security Checklist for Vibe-Coded Apps (2026)
Supabase Security Checklist for Vibe-Coded Apps (2026) A vibe-coded app can look finished long before it is safe. The interface works, sign-in works, and data appears where it should. What is easy to miss is that the same setup also lets the wrong people reach that data, because Supabase’s safety does not come from hiding […]
Is It Safe to Expose Your Supabase Anon Key? (Only If RLS Is On)
Is It Safe to Expose Your Supabase Anon Key? (Only If RLS Is On) Yes — with one condition that does all the work. The Supabase anon key, now called the publishable key in new projects, is designed to be public. It ships inside your app’s JavaScript, so every visitor already has a copy. That […]
Supabase “RLS Disabled in Public” Warning: What It Means and How to Fix It
If you open the Supabase Security Advisor and see “RLS Disabled in Public”, it means a table in your project’s public schema has Row Level Security (RLS) switched off. In plain terms: the database is not checking which rows a request is allowed to see before it answers. If that table can be reached through […]