Best VPN for Pakistan in 2026 – Top 10 Tested, Ranked & Actually Working
Why You Need a VPN in Pakistan Right Now If you’re in Pakistan and trying to use the internet freely in 2026, you already know the pain. Websites blocked. Apps throttled. Social media gone during protests. And the list keeps growing every year. The Pakistan Telecommunication Authority (PTA) has built one of the most aggressive […]
How to Test Supabase RLS Policies (Free RLS Tester Options Compared)
Row Level Security is the lock on your Supabase database. It decides which rows each person can read, add, change or delete. The trouble is that a policy can look right, sit in the right dashboard, and still leak — and nothing in the dashboard will tell you. The only way to know is to […]
How to Secure a Vibe-Coded App: A Non-Technical Founder’s Guide
You built an app by describing it to an AI tool — Lovable, Bolt, Replit, v0, Cursor or Claude Code — and it works. The screens look finished, the buttons do what you asked, and friends who tried it said it feels like a real product. That is exactly the moment to ask the question […]
Netlify “Exposed Secrets Detected”: How to Fix a Failed Build Safely
Your build failed, and the deploy log says a secret was detected. Nothing is live, nothing is broken for your visitors, and that is the point: Netlify stopped the deploy before the secret reached the public internet. The fix is not to turn the scan off and push again. It is to work out what […]
Lovable Security Issues: The 7 Mistakes We See Most Often
Lovable apps keep leaking the same way. In November 2026, the Hamburg security firm Crissy Field published a study of 159,041 Lovable projects and found personal data — passport numbers, payment records, more than 200,000 private chat messages — readable without logging in. Nobody hacked Lovable, and nobody hacked Supabase. The apps’ own database rules […]
Firebase Security Rules Auditor: How to Audit Your Rules for Free
Your Firebase API key is public by design, and that is fine. What decides who can read or change your users’ data is a short file you may never have looked at: your Firebase Security Rules. Auditing them means reading that file, checking it for the patterns that leak data, and then proving — with […]
“API Key Exposure Detected in Your Repository”: What the Alert Means and How to Clean Up
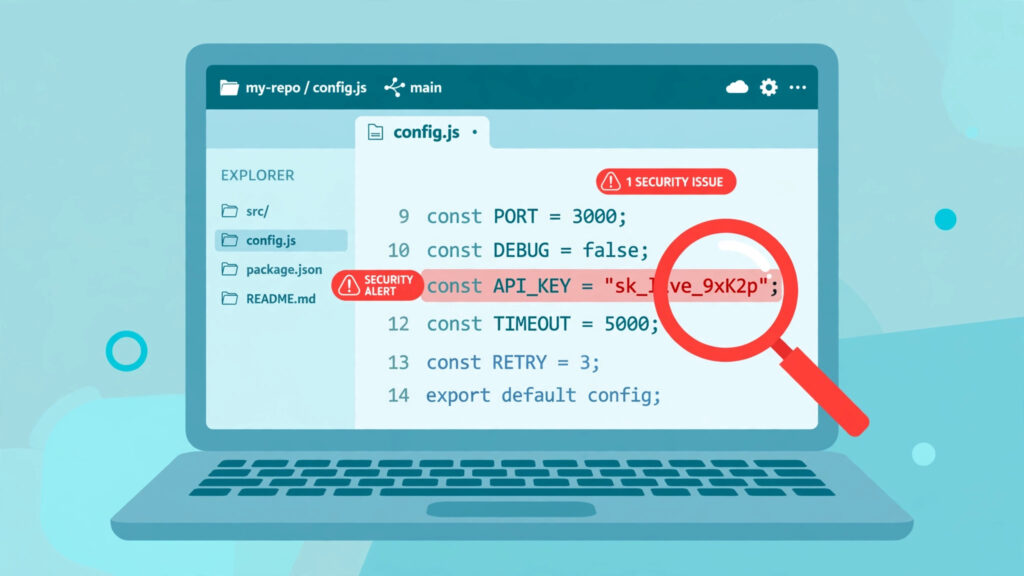
You got an alert: an API key was detected in your repository. The short answer is: treat the key as compromised, revoke it now, and read the alert properly before you do anything else. Deleting the file or the commit does not fix it. The key is still in your git history, in forks and […]
OpenAI API Key Exposed? What to Do in the Next Hour
Your OpenAI API key is exposed. The short answer is: revoke it first, and do it now. Everything else — the replacement key, the usage check, the spending cap, finding how it leaked — comes after, because none of it matters while the old key still works. An OpenAI API key is a bearer credential. […]
Copy-Paste Security Prompts for Vibe Coders (Cursor, Lovable, Replit, Claude)
“Make it secure” is the most common security prompt in vibe coding, and it is also the least useful. An AI coding assistant told to “make it secure” will do something that looks secure: it will add a login page, hash a password, maybe even write a comment saying the code is safe. What it […]
Is Your Lovable App Leaking the Supabase Service Role Key?
Yes, it might be — and this is the one leak in a Lovable app that no database setting can save you from. The Supabase service role key bypasses every Row Level Security rule you have. If it has reached your app’s browser bundle, anyone who opens your site can read, change or delete every […]
Vibe-Coded App Security Checklist: 25 Checks Before You Launch
This is the vibe-coded app security checklist to run before you launch: 25 checks across six areas — secrets, database rules, auth, money, input and code, and launch readiness. How to use this checklist The critical eight are the launch gate. Checks 1, 5, 6, 10, 12, 14, 15 and 22 are marked ★ below. […]