What Happens If Your API Key Is Exposed? Real Costs and a 10-Minute Fix Plan
This is what happens if an API key is exposed: anyone who finds it can use it as if they were your app. An API key is a password your code uses to log in to another service, and most keys carry no second check — no login prompt, no confirmation, no way for the […]
Is a .env File Secure? What It Protects and What It Doesn’t
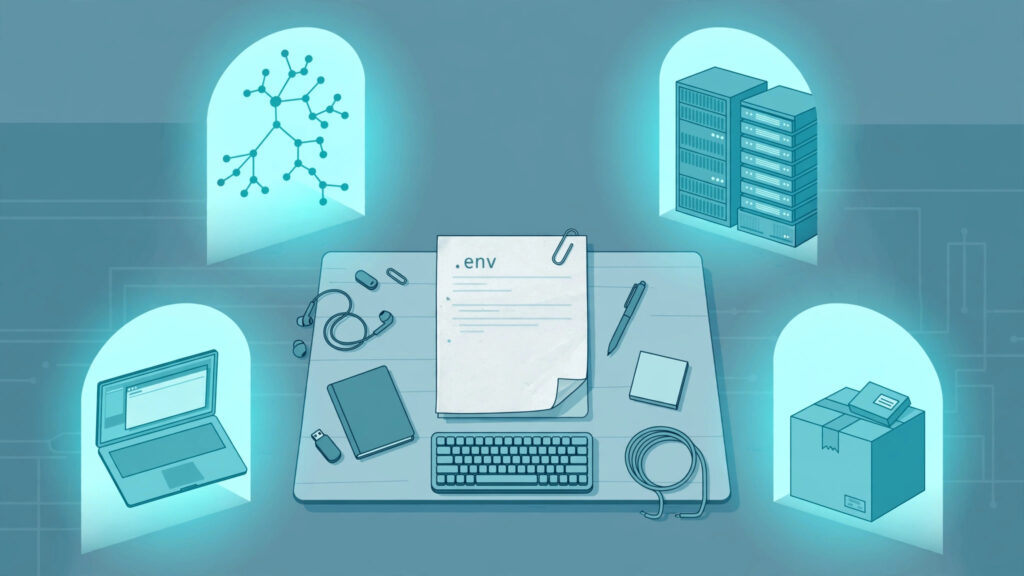
No — not on its own. A .env file is a plain text file. It has no encryption, no password, no access control and no record of who read it. Anything that can open the file can read every secret in it, in clear text. That does not make it useless. A .env file protects […]
How to Keep API Keys Away From Claude Code, Cursor and Other AI Agents
Yes — but not with a single setting. An API key reaches an AI coding agent through three different routes, and each one needs its own fix. A .gitignore entry stops git from committing your .env file. It does nothing about the agent reading that same file while it works, nothing about a key you […]
Is the Firebase API Key Secret? What Really Protects Your Data
No. The Firebase API key is not a secret. It is a public identifier that tells Google which Firebase project your app belongs to. It ships inside your app’s code, anyone who opens your app can read it, and Firebase’s own documentation says that is fine. What protects your data is not the key. It […]
Firebase API Key Exposed on GitHub: Is It Actually a Problem?
Your Firebase API key is on GitHub, and GitHub — or a scanner, or a worried teammate — has flagged it. The short answer is: usually not a problem by itself, but it is a problem if the things behind the key are not locked down. The key is not a password. It is a […]
How to Hide an API Key From the Browser Network Tab (and Why You Can’t)
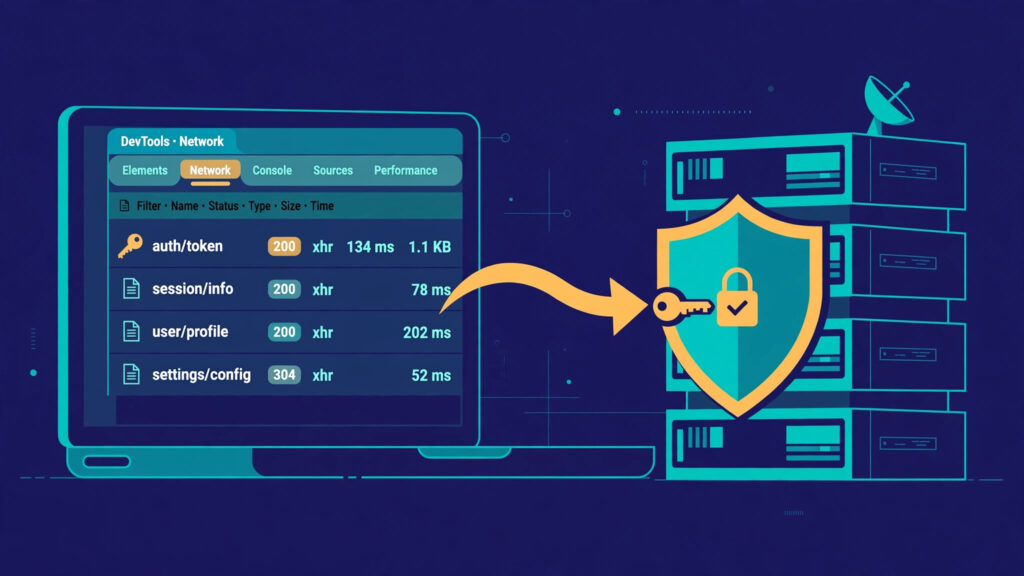
How to Hide an API Key From the Browser Network Tab (and Why You Can’t) You cannot hide an API key from the browser’s Network tab if the browser itself sends that key. The Network tab is not a leak in the browser. It is the browser showing its owner exactly what it sent and […]
Is French Stream Safe? Everything You Need to Know [2026]
Is French Stream Safe? What 2026 Scans Show and What to Do Instead No, French Stream isn’t reliably safe. It’s a name used by many clone domains with no verified owner, and several of them have been blacklisted by security vendors. The sites also stream films and series without licenses, and a Paris court ordered […]
Free Security Scanner for Vibe-Coded Apps: Check Yours in 60 Seconds
A vibe-coded app can work perfectly and still be open. That is the whole problem: an AI builder will happily ship a working sign-in page, a working dashboard, and a database that answers anyone who asks. Nothing breaks, so nothing warns you. A free security scanner is the fastest way to find out whether that […]
Supabase Security Checklist for Vibe-Coded Apps (2026)
Supabase Security Checklist for Vibe-Coded Apps (2026) A vibe-coded app can look finished long before it is safe. The interface works, sign-in works, and data appears where it should. What is easy to miss is that the same setup also lets the wrong people reach that data, because Supabase’s safety does not come from hiding […]
Is It Safe to Expose Your Supabase Anon Key? (Only If RLS Is On)
Is It Safe to Expose Your Supabase Anon Key? (Only If RLS Is On) Yes — with one condition that does all the work. The Supabase anon key, now called the publishable key in new projects, is designed to be public. It ships inside your app’s JavaScript, so every visitor already has a copy. That […]